Enterprise Azure Architect
Azure enterprise infra planner
Architect and provision enterprise Azure infrastructure from workload descriptions. For cloud architects and platform engineers planning networking, identity, security, compliance, and multi-resource topologies with WAF alignment.
---
name: azure-enterprise-infra-planner
description: "Architect and provision enterprise Azure infrastructure from workload descriptions. For cloud architects and platform engineers planning networking, identity, security, compliance, and multi-resource topologies with WAF alignment. Generates Bicep or Terraform directly (no azd). WHEN: 'plan Azure infrastructure', 'architect Azure landing zone', 'design hub-spoke network', 'plan multi-region DR topology', 'set up VNets firewalls and private endpoints', 'subscription-scope Bicep deployment', 'Azure Backup for VM workloads'. PREFER azure-prepare FOR app-centric workflows."
license: MIT
metadata:
  author: Microsoft
  version: "1.4.2"
---

# Azure Enterprise Infra Planner

## When to Use This Skill

Activate this skill when user wants to:
- Plan enterprise Azure infrastructure from a workload or architecture description
- Architect a landing zone, hub-spoke network, or multi-region topology
- Design networking infrastructure: VNets, subnets, firewalls, private endpoints, VPN gateways
- Plan identity, RBAC, and compliance-driven infrastructure
Overview
Activate this skill when user wants to: - Plan enterprise Azure infrastructure from a workload or architecture description - Architect a landing zone, hub-spoke network, or multi-region topology - Design networking infrastructure: VNets, subnets, firewalls, private endpoints, VPN gateways - Plan identity, RBAC, and compliance-driven infrastructure - Generate Bicep or Terraform for subscription-scope or multi-resource-group deployments - Plan disaster recovery, failover, or cross-region high-availability topologies
Manual install (npx, ZIP)
npx skills add microsoft/skills --skill azure-enterprise-infra-planner -g -a claude-codenpx degit microsoft/skills/.github/plugins/azure-skills/skills/azure-enterprise-infra-planner#main ~/.claude/skills/azure-enterprise-infra-plannerConnects with Agent Alley MCP · agentalley.io/mcp
Files included
SKILL.md6.2 KB
Read SKILL.md here
Show the full text107 lines
Azure Enterprise Infra Planner
When to Use This Skill
Activate this skill when user wants to:
- Plan enterprise Azure infrastructure from a workload or architecture description
- Architect a landing zone, hub-spoke network, or multi-region topology
- Design networking infrastructure: VNets, subnets, firewalls, private endpoints, VPN gateways
- Plan identity, RBAC, and compliance-driven infrastructure
- Generate Bicep or Terraform for subscription-scope or multi-resource-group deployments
- Plan disaster recovery, failover, or cross-region high-availability topologies
Quick Reference
| Property | Details |
|---|---|
| MCP tools | insights_get, get_azure_bestpractices_get, wellarchitectedframework_serviceguide_get, microsoft_docs_fetch, microsoft_docs_search, bicepschema_get |
| CLI commands | az deployment group create, az bicep build, az resource list, terraform init, terraform plan, terraform validate, terraform apply, checkov |
| Output schema | schema.md |
| Key references | workflow.md, waf-checklist.md, resources/, constraints/ |
Workflow (Start Here)
Follow the step-by-step instructions in workflow.md to execute the 7 phases of infrastructure planning and provisioning.
Architecture
The skill runs a 7-phase, gated pipeline. Input is triaged into one of two flows:
- Greenfield — only new requirements; run the phases straight through.
- Referenced (brownfield) — the user supplies something that already exists (a live resource / resource group / subscription, IaC or an infra plan, or a requirements doc). The same phases run, plus referenced-workload.md: existing resources are inventoried and referenced (never recreated), the new workload is wired into them, and Phase 7 deploys additively (incremental only — never modifying or destroying the referenced resources).
Every phase advances only after its gate passes. Phase 5 requires explicit user approval; Phase 6 is a
hardened, self-verifying gate — the generated IaC must be secure-by-default, pass local validation
(az bicep build / terraform validate) with zero errors, pass a checkov security scan with no
unresolved high/critical findings, and the skill must show the command output and emit a completion
self-check before advancing; Phase 7 requires an explicit, risk-acknowledged deploy confirmation.
flowchart TD
    IN([Input]) --> TRIAGE{Existing infra<br/>referenced?}
    TRIAGE -- "No (greenfield)" --> P1
    TRIAGE -- "Yes (referenced)" --> RW[/referenced-workload.md:<br/>inventory + assign roles<br/>reference, never recreate/]
    RW --> P1

    subgraph PIPE [7-phase gated pipeline]
        direction TB
        P1[Phase 1 · Extract insights] --> P2[Phase 2 · Research best practices]
        P2 --> P3[Phase 3 · Research resources]
        P3 --> P4[Phase 4 · Generate plan]
        P4 --> P5{Phase 5 · Verify<br/>user approves?}
        P5 -- "no" --> P4
        P5 -- "approved" --> P6[Phase 6 · Generate IaC]
        P6 --> VAL{Validate<br/>az bicep build /<br/>terraform validate}
        VAL -- "errors" --> P6
        VAL -- "clean" --> P7{Phase 7 · Deploy<br/>risk-ack confirm?}
    end

    P7 -- "greenfield" --> DEP[az deployment / terraform apply]
    P7 -- "referenced" --> DEPADD[Additive deploy · incremental only<br/>what-if preview · no destroy of<br/>referenced resources]
    DEP --> OUT([Deployed])
    DEPADD --> OUT

    classDef gate fill:#fff3cd,stroke:#d39e00,color:#000;
    classDef ref fill:#e2f0d9,stroke:#548235,color:#000;
    class P5,VAL,P7,TRIAGE gate;
    class RW,DEPADD ref;
Artifacts (written under <project-root>/): .azure/insights.json (Phase 1),
.azure/infrastructure-plan.json (Phase 4, status draft→approved→deployed), and
infra/main.bicep + infra/modules/* or infra/main.tf + infra/modules/** (Phase 6).
MCP Tools
| Tool | Purpose |
|---|---|
insights_get |
Retrieve insights about the user's existing Azure environment to guide planning decisions |
get_azure_bestpractices_get |
Azure best practices for code generation, operations, and deployment |
wellarchitectedframework_serviceguide_get |
WAF service guide for a specific Azure service |
microsoft_docs_search |
Search Microsoft Learn for relevant documentation chunks |
microsoft_docs_fetch |
Fetch full content of a Microsoft Learn page by URL |
bicepschema_get |
Bicep schema definition for any Azure resource type (latest API version) |
Error Handling
| Error | Cause | Fix |
|---|---|---|
| MCP tool error or not available | Tool call timeout, connection error, or tool doesn't exist | Retry once; fall back to reference files and notify user if unresolved |
| Plan approval missing | meta.status is not approved |
Stop and prompt user for approval before IaC generation or deployment |
| IaC validation failure | az bicep build or terraform validate returns errors |
Fix the generated code and re-validate; notify user if unresolved |
| Pairing constraint violation | Incompatible SKU or resource combination | Fix in plan before proceeding to IaC generation |
| Infra plan or IaC files not found | Files written to wrong location or not created | Verify files exist at <project-root>/.azure/ and <project-root>/infra/; if missing, re-create the files by following workflow.md exactly |
| 1 | |
| 2 | name azure-enterprise-infra-planner |
| 3 | description "Architect and provision enterprise Azure infrastructure from workload descriptions. For cloud architects and platform engineers planning networking, identity, security, compliance, and multi-resource topologies with WAF alignment. Generates Bicep or Terraform directly (no azd). WHEN: 'plan Azure infrastructure', 'architect Azure landing zone', 'design hub-spoke network', 'plan multi-region DR topology', 'set up VNets firewalls and private endpoints', 'subscription-scope Bicep deployment', 'Azure Backup for VM workloads'. PREFER azure-prepare FOR app-centric workflows." |
| 4 | license MIT |
| 5 | metadata |
| 6 | author Microsoft |
| 7 | version "1.4.2" |
| 8 | |
| 9 | |
| 10 | # Azure Enterprise Infra Planner |
| 11 | |
| 12 | ## When to Use This Skill |
| 13 | |
| 14 | Activate this skill when user wants to: |
| 15 | Plan enterprise Azure infrastructure from a workload or architecture description |
| 16 | Architect a landing zone, hub-spoke network, or multi-region topology |
| 17 | Design networking infrastructure: VNets, subnets, firewalls, private endpoints, VPN gateways |
| 18 | Plan identity, RBAC, and compliance-driven infrastructure |
| 19 | Generate Bicep or Terraform for subscription-scope or multi-resource-group deployments |
| 20 | Plan disaster recovery, failover, or cross-region high-availability topologies |
| 21 | |
| 22 | ## Quick Reference |
| 23 | |
| 24 | | Property | Details | |
| 25 | |---|---| |
| 26 | | MCP tools | `insights_get`, `get_azure_bestpractices_get`, `wellarchitectedframework_serviceguide_get`, `microsoft_docs_fetch`, `microsoft_docs_search`, `bicepschema_get` | |
| 27 | | CLI commands | `az deployment group create`, `az bicep build`, `az resource list`, `terraform init`, `terraform plan`, `terraform validate`, `terraform apply`, `checkov` | |
| 28 | | Output schema | [schema.md] | |
| 29 | | Key references | [workflow.md], [waf-checklist.md], [resources/], [constraints/] | |
| 30 | |
| 31 | ## Workflow (Start Here) |
| 32 | |
| 33 | Follow the step-by-step instructions in [workflow.md] to execute the 7 phases of infrastructure planning and provisioning. |
| 34 | |
| 35 | ## Architecture |
| 36 | |
| 37 | The skill runs a **7-phase, gated pipeline**. Input is triaged into one of two flows: |
| 38 | |
| 39 | **Greenfield** — only new requirements; run the phases straight through. |
| 40 | **Referenced (brownfield)** — the user supplies something that already exists (a live resource / |
| 41 | resource group / subscription, IaC or an infra plan, or a requirements doc). The same phases run, plus |
| 42 | [referenced-workload.md]: existing resources are inventoried and |
| 43 | referenced (never recreated), the new workload is wired into them, and **Phase 7 deploys additively** |
| 44 | (incremental only — never modifying or destroying the referenced resources). |
| 45 | |
| 46 | Every phase advances only after its gate passes. Phase 5 requires explicit user approval; **Phase 6 is a |
| 47 | hardened, self-verifying gate** — the generated IaC must be secure-by-default, pass local validation |
| 48 | (`az bicep build` / `terraform validate`) with zero errors, pass a `checkov` security scan with no |
| 49 | unresolved high/critical findings, and the skill must **show the command output** and emit a completion |
| 50 | self-check before advancing; Phase 7 requires an explicit, risk-acknowledged deploy confirmation. |
| 51 | |
| 52 | |
| 53 | flowchart TD |
| 54 | IN([Input]) --> TRIAGE{Existing infra<br/>referenced?} |
| 55 | TRIAGE -- "No (greenfield)" --> P1 |
| 56 | TRIAGE -- "Yes (referenced)" --> RW[/referenced-workload.md:<br/>inventory + assign roles<br/>reference, never recreate/] |
| 57 | RW --> P1 |
| 58 | |
| 59 | subgraph PIPE [7-phase gated pipeline] |
| 60 | direction TB |
| 61 | P1[Phase 1 · Extract insights] --> P2[Phase 2 · Research best practices] |
| 62 | P2 --> P3[Phase 3 · Research resources] |
| 63 | P3 --> P4[Phase 4 · Generate plan] |
| 64 | P4 --> P5{Phase 5 · Verify<br/>user approves?} |
| 65 | P5 -- "no" --> P4 |
| 66 | P5 -- "approved" --> P6[Phase 6 · Generate IaC] |
| 67 | P6 --> VAL{Validate<br/>az bicep build /<br/>terraform validate} |
| 68 | VAL -- "errors" --> P6 |
| 69 | VAL -- "clean" --> P7{Phase 7 · Deploy<br/>risk-ack confirm?} |
| 70 | end |
| 71 | |
| 72 | P7 -- "greenfield" --> DEP[az deployment / terraform apply] |
| 73 | P7 -- "referenced" --> DEPADD[Additive deploy · incremental only<br/>what-if preview · no destroy of<br/>referenced resources] |
| 74 | DEP --> OUT([Deployed]) |
| 75 | DEPADD --> OUT |
| 76 | |
| 77 | classDef gate fill:#fff3cd,stroke:#d39e00,color:#000; |
| 78 | classDef ref fill:#e2f0d9,stroke:#548235,color:#000; |
| 79 | class P5,VAL,P7,TRIAGE gate; |
| 80 | class RW,DEPADD ref; |
| 81 | |
| 82 | |
| 83 | **Artifacts** (written under `<project-root>/`): `.azure/insights.json` (Phase 1), |
| 84 | `.azure/infrastructure-plan.json` (Phase 4, status `draft`→`approved`→`deployed`), and |
| 85 | `infra/main.bicep` + `infra/modules/*` or `infra/main.tf` + `infra/modules/**` (Phase 6). |
| 86 | |
| 87 | ## MCP Tools |
| 88 | |
| 89 | | Tool | Purpose | |
| 90 | |------|---------| |
| 91 | | `insights_get` | Retrieve insights about the user's existing Azure environment to guide planning decisions | |
| 92 | | `get_azure_bestpractices_get` | Azure best practices for code generation, operations, and deployment | |
| 93 | | `wellarchitectedframework_serviceguide_get` | WAF service guide for a specific Azure service | |
| 94 | | `microsoft_docs_search` | Search Microsoft Learn for relevant documentation chunks | |
| 95 | | `microsoft_docs_fetch` | Fetch full content of a Microsoft Learn page by URL | |
| 96 | | `bicepschema_get` | Bicep schema definition for any Azure resource type (latest API version) | |
| 97 | |
| 98 | ## Error Handling |
| 99 | |
| 100 | | Error | Cause | Fix | |
| 101 | |---|---|---| |
| 102 | | MCP tool error or not available | Tool call timeout, connection error, or tool doesn't exist | Retry once; fall back to reference files and notify user if unresolved | |
| 103 | | Plan approval missing | `meta.status` is not `approved` | Stop and prompt user for approval before IaC generation or deployment | |
| 104 | | IaC validation failure | `az bicep build` or `terraform validate` returns errors | Fix the generated code and re-validate; notify user if unresolved | |
| 105 | | Pairing constraint violation | Incompatible SKU or resource combination | Fix in plan before proceeding to IaC generation | |
| 106 | | Infra plan or IaC files not found | Files written to wrong location or not created | Verify files exist at `<project-root>/.azure/` and `<project-root>/infra/`; if missing, re-create the files by following [workflow.md] exactly | |
| 107 |
Details
- License
- MIT
- Stars on the repo
- ★ 3,077
- Checked
- Source
- microsoft/skills ↗
- Creator
- microsoft · 31 listings
Similar skills
See all → SkillAzure App Deployer
 microsoft/skills · by microsoftEnd-to-end orchestrator: from a business idea, app idea, or existing app to running Azure deployment with cost estimates and pre-deploy approval. Analyzes your app, auto-detects the right Azure services, scaffolds infrastructure code, and deploys — tailored to your app, not a template. Handles moving existing apps to Azure without rewriting or with minimal changes. WHEN: bring your app to Azure, plan my app, cost to run, is my code ready to deploy, deploy my app to the cloud, deploy all my services, what Azure services do I need, plan my Azure deployment, deploy my new app to Azure, one-click deploy, I have an app and want it on Azure, migrate my app to Azure, help me get started, build an app, no code yet, starter project. DO NOT USE FOR: use azd for deployment(use azure-deploy), optimizing existing costs (use cost-optimization), code readiness checks only (use azure-app-onboard-prereq).★ 3.1k GitHub stars
 SkillAzure Deployment Auditormicrosoft/skills · by microsoftAssess whether source code is ready to deploy to Azure — the check BEFORE infrastructure work. Evaluates build health, app completeness, dependencies and local services, stack compatibility, and deployment feasibility. Answers questions about what your app needs before it can be deployed — frameworks, dependencies, and configuration. Checks whether dependencies are compatible and identifies deployment blockers and unsupported frameworks. WHEN: "evaluate my repo", "is my app ready to deploy", "what does my app need to deploy", "what do I need before deploying", "does my app need", "can I ship this to Azure", "scan my repo for issues", "is this app deployable", "check if my app is ready for Azure", "do I need a Dockerfile", "what's blocking my deployment", "are there any blockers", "are my dependencies compatible", "does Azure support my framework", "what needs to change before deploying", "check my app configuration".★ 3.1k GitHub stars
 SkillAzure AI Gatewaymicrosoft/azure-skills · by microsoftConfigure Azure API Management as an AI Gateway for AI models, MCP tools, and agents. WHEN: semantic caching, token limit, content safety, load balancing, AI model governance, MCP rate limiting, jailbreak detection, add Azure OpenAI backend, add AI Foundry model, test AI gateway, LLM policies, configure AI backend, token metrics, AI cost control, convert API to MCP, import OpenAPI to gateway.★ 1.6k GitHub stars
 SkillKusto Query Buildermicrosoft/azure-skills · by microsoftQuery and analyze data in Azure Data Explorer (Kusto/ADX) using KQL for log analytics, telemetry, and time series analysis. WHEN: KQL queries, Kusto database queries, Azure Data Explorer, ADX clusters, log analytics, time series data, IoT telemetry, anomaly detection.★ 1.6k GitHub stars
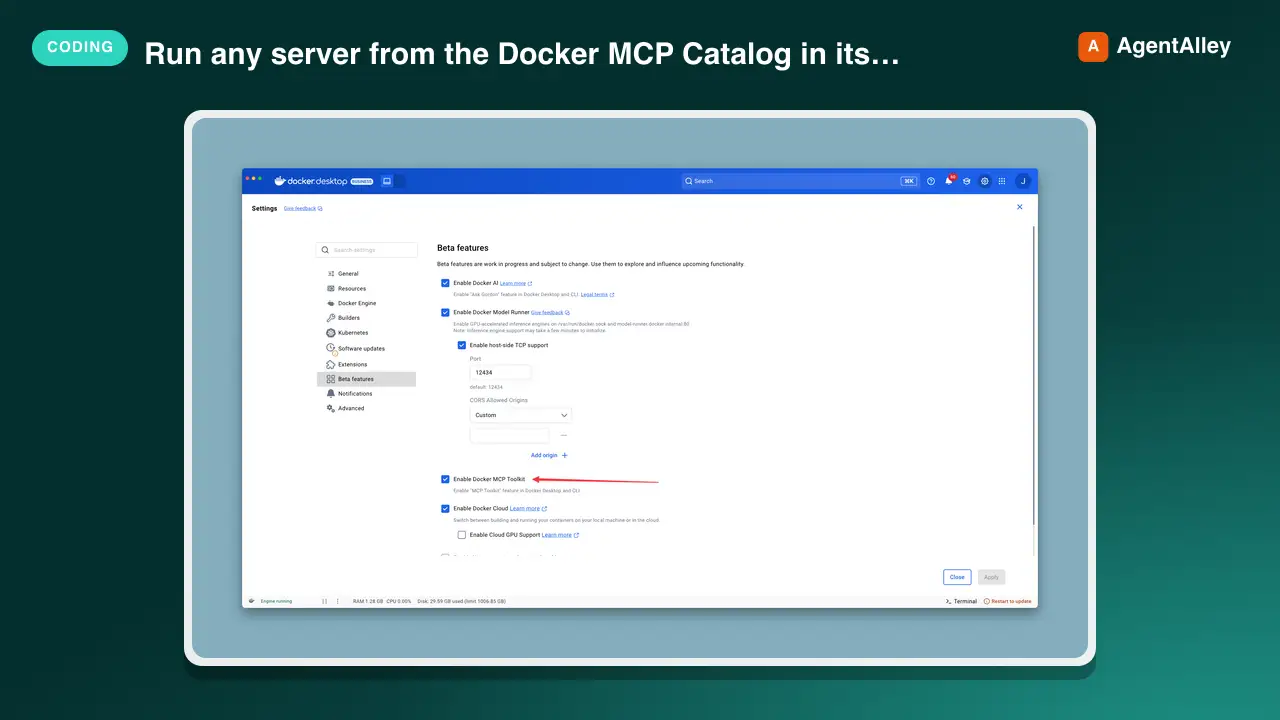 AgentDocker CLI Container Gateway
 docker/mcp-gateway · by dockerDocker's own CLI plugin: run any server from the Docker MCP Catalog in its own container, behind one connection, with secrets kept out of env vars.★ 1.6k GitHub stars
 AgentAgent Marketplace
 elisymlabs/elisym · by elisymlabsOpen infrastructure for AI agents to discover and pay each other★ 17 GitHub stars
More from microsoft
 AgentPlaywright Browser Automation MCPmicrosoft/playwright-mcp · by microsoftMicrosoft's browser automation server: your AI opens pages, clicks, fills forms and reads the page through the accessibility tree.★ 37.5k GitHub stars
 SkillUsage-Based Agent Trainermicrosoft/SkillOpt · by microsoftUse when the user wants their Claude agent to self-improve from past usage, asks about a nightly/offline 'sleep' or 'dream' cycle, memory/skill consolidation, or says things like 'make my agent better the more I use it', 'review my past sessions', 'learn my pr★ 17.3k GitHub starsSkillAzure App Deployermicrosoft/skills · by microsoftEnd-to-end orchestrator: from a business idea, app idea, or existing app to running Azure deployment with cost estimates and pre-deploy approval. Analyzes your app, auto-detects the right Azure services, scaffolds infrastructure code, and deploys — tailored to your app, not a template. Handles moving existing apps to Azure without rewriting or with minimal changes. WHEN: bring your app to Azure, plan my app, cost to run, is my code ready to deploy, deploy my app to the cloud, deploy all my services, what Azure services do I need, plan my Azure deployment, deploy my new app to Azure, one-click deploy, I have an app and want it on Azure, migrate my app to Azure, help me get started, build an app, no code yet, starter project. DO NOT USE FOR: use azd for deployment(use azure-deploy), optimizing existing costs (use cost-optimization), code readiness checks only (use azure-app-onboard-prereq).★ 3.1k GitHub starsSkillAzure Deployment Auditormicrosoft/skills · by microsoftAssess whether source code is ready to deploy to Azure — the check BEFORE infrastructure work. Evaluates build health, app completeness, dependencies and local services, stack compatibility, and deployment feasibility. Answers questions about what your app needs before it can be deployed — frameworks, dependencies, and configuration. Checks whether dependencies are compatible and identifies deployment blockers and unsupported frameworks. WHEN: "evaluate my repo", "is my app ready to deploy", "what does my app need to deploy", "what do I need before deploying", "does my app need", "can I ship this to Azure", "scan my repo for issues", "is this app deployable", "check if my app is ready for Azure", "do I need a Dockerfile", "what's blocking my deployment", "are there any blockers", "are my dependencies compatible", "does Azure support my framework", "what needs to change before deploying", "check my app configuration".★ 3.1k GitHub stars
 SkillAzure Security Auditormicrosoft/skills · by microsoftRun Azure compliance and security audits with azqr plus Key Vault expiration checks. Covers best-practice assessment, resource review, policy/compliance validation, and security posture checks. WHEN: compliance scan, security audit, BEFORE running azqr (compliance cli tool), Azure best practices, Key Vault expiration check, expired certificates, expiring secrets, orphaned resources, compliance assessment.★ 3.1k GitHub starsSkillAzure AI Gatewaymicrosoft/azure-skills · by microsoftConfigure Azure API Management as an AI Gateway for AI models, MCP tools, and agents. WHEN: semantic caching, token limit, content safety, load balancing, AI model governance, MCP rate limiting, jailbreak detection, add Azure OpenAI backend, add AI Foundry model, test AI gateway, LLM policies, configure AI backend, token metrics, AI cost control, convert API to MCP, import OpenAPI to gateway.★ 1.6k GitHub stars